Establishing a robust AI agent governance framework is crucial for operational leaders integrating managed AI agents into workflows. This framework moves beyond abstract principles, translating them into concrete controls and accountable routines to manage risk and ensure beneficial outcomes.
Effective governance ensures that AI agents operate reliably, ethically, and in alignment with organizational objectives. It provides the necessary structure for oversight, auditability, and human review, fostering trust and maximizing the operational capacity gained from AI deployments.
Defining Governance Layers and Decision Rights
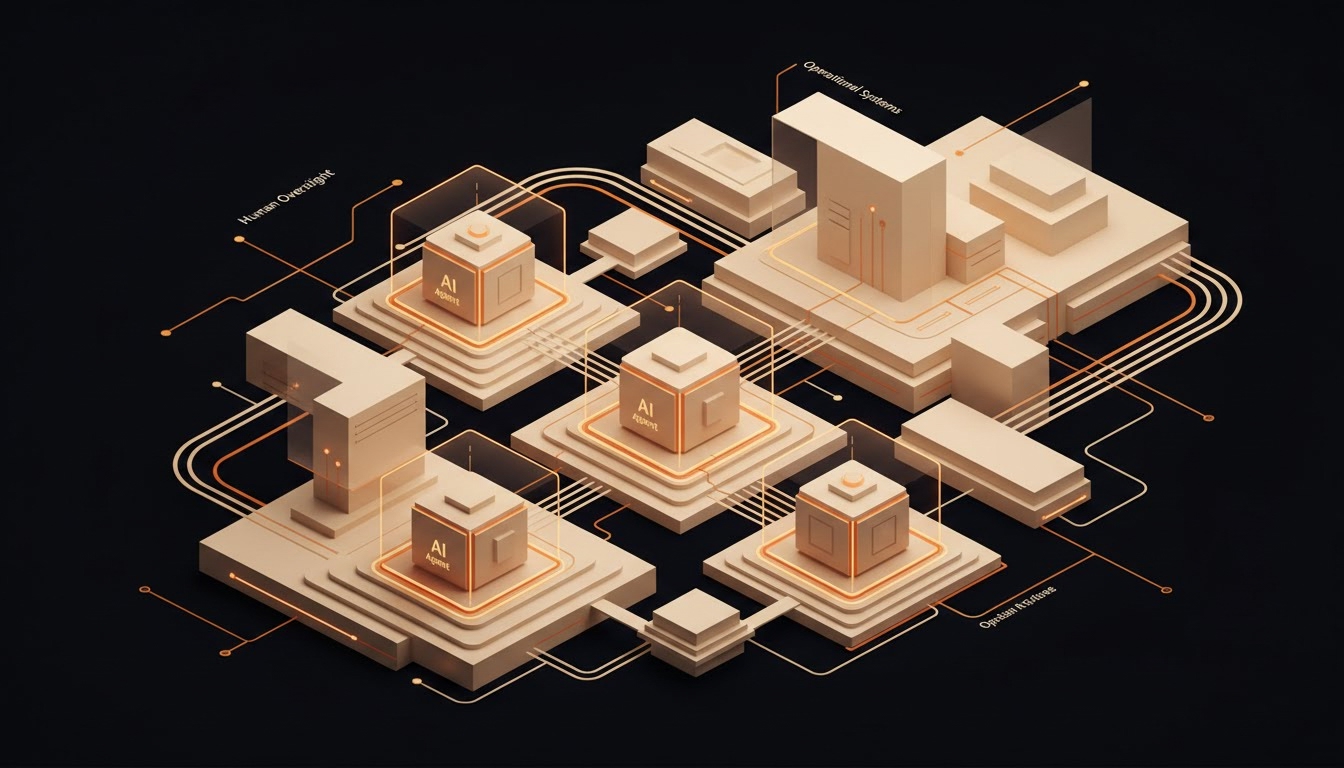
Effective AI agent governance requires a tiered structure, clearly delineating responsibilities across strategic, tactical, and operational levels. The strategic layer sets the overarching AI vision and risk appetite, while the tactical layer translates these into specific policies and standards for AI agent deployment.
The operational layer, where managed AI agents execute tasks, focuses on day-to-day oversight and adherence to established controls. Clear decision rights must be assigned at each layer, specifying who approves agent design, deployment, modifications, and exceptions, ensuring accountability and preventing unauthorized actions.
- Strategic: Sets vision, risk appetite.
- Tactical: Defines policies, standards.
- Operational: Day-to-day oversight, controls.
- Decision rights: Who approves what, when.
Translating Principles into Named Controls
Governance principles, such as fairness, transparency, and accountability, must be operationalized into specific, named controls. These controls are the practical rules that dictate how AI agents function within an organization's workflows, ensuring alignment with ethical guidelines and regulatory expectations.
For example, a 'Data Minimization Control' would specify that an AI agent only accesses data strictly necessary for its task. Similarly, a 'Human Override Control' would define the conditions and process for human intervention, ensuring that human review remains an integral part of the system.
- Principles become actionable rules.
- Example: Data Minimization Control.
- Example: Human Override Control.
- Ensures ethical and regulatory alignment.
Establishing Evidence Requirements for Auditability
To ensure accountability and trust, every AI agent's operation must generate verifiable evidence. This evidence forms the basis for auditing, allowing organizations to trace decisions, assess performance, and confirm compliance with established controls and policies.
Evidence requirements include detailed logs of data access, task execution, human interventions, and performance metrics. These audit trails are critical for diagnosing issues, demonstrating regulatory compliance, and building confidence in the managed AI agents' operational integrity.
- Verifiable evidence for every operation.
- Trace decisions, assess performance.
- Logs: data access, task execution, human intervention.
- Critical for compliance and trust.
Defining Accountable Human Review Cadence
Human review is indispensable for maintaining oversight and ensuring managed AI agents operate as intended, especially in dynamic environments. Establishing a clear, accountable human review cadence means defining how often, by whom, and under what conditions AI agent performance and outputs are assessed.
This cadence can vary from daily spot-checks for high-risk workflows to monthly performance reviews for stable operations. The review process must include mechanisms for feedback, corrective action, and escalation, ensuring that human insight continuously refines and governs AI agent behaviour.
- Human review is indispensable.
- Define frequency, personnel, conditions.
- Cadence varies by risk and stability.
- Includes feedback, correction, escalation.
Integrating Governance with Existing Risk Management
An AI agent governance framework should not exist in isolation but be integrated into an organization's broader enterprise risk management (ERM) strategy. This ensures that AI-specific risks, such as algorithmic bias or operational drift, are assessed and managed alongside other business risks.
The NIST AI Risk Management Framework [1] provides a voluntary guide for incorporating trustworthiness considerations into AI systems, emphasizing functions like GOVERN, MAP, MEASURE, and MANAGE. Aligning AI agent governance with these established practices strengthens overall organizational resilience and control.
- Integrate with enterprise risk management.
- Manage AI-specific risks proactively.
- Align with NIST AI RMF functions [1].
- Strengthens overall organizational control.
Implementing a controls-based AI agent governance framework is not merely a compliance exercise; it is fundamental to building trust and realizing the full operational capacity of managed AI agents. By clearly defining governance layers, translating principles into named controls, establishing evidence requirements, and setting accountable human review cadences, organizations can confidently integrate AI into their most critical workflows.
This pragmatic approach ensures that AI agents operate responsibly, are auditable, and remain aligned with strategic objectives, transforming potential risks into reliable operational advantages. Leaders who proactively embed robust governance will unlock sustainable value from their AI investments.
Frequently asked questions
How do AI agent governance layers differ from traditional IT governance?
AI agent governance layers specifically address the unique risks and complexities of autonomous or semi-autonomous systems. While traditional IT governance focuses on infrastructure and data, AI governance adds layers for algorithmic transparency, bias mitigation, and dynamic human-AI interaction oversight, requiring distinct decision rights.
What is the role of human review when AI agents are designed for autonomy?
Even highly autonomous AI agents require human review. This ensures ongoing alignment with organizational goals, identifies performance degradation, and allows for intervention in unforeseen circumstances. Human review shifts from direct task execution to oversight, exception handling, and strategic guidance, maintaining accountability.
How can I ensure AI agent governance is practical, not just theoretical?
To be practical, governance must translate principles into specific, named controls with clear evidence requirements and defined review cadences. Focus on integrating these controls directly into existing workflow processes and assigning explicit decision rights to functional leaders, making governance an operational routine, not an abstract policy.
What evidence should I collect for AI agent auditability?
For auditability, collect comprehensive logs of data accessed, tasks executed, decisions made (including confidence scores), human interventions, and performance metrics. Document all model updates, configuration changes, and any exceptions or errors encountered. This creates a traceable record of the AI agent's operational history.
How does Kaza support AI agent governance?
Kaza deploys managed AI agents and automations, diagnosing workflows and designing systems that integrate into existing tools. While Kaza provides the operational capacity, establishing the overarching governance framework, defining specific controls, and setting review cadences remains an organizational responsibility to ensure alignment with internal policies and risk appetite.