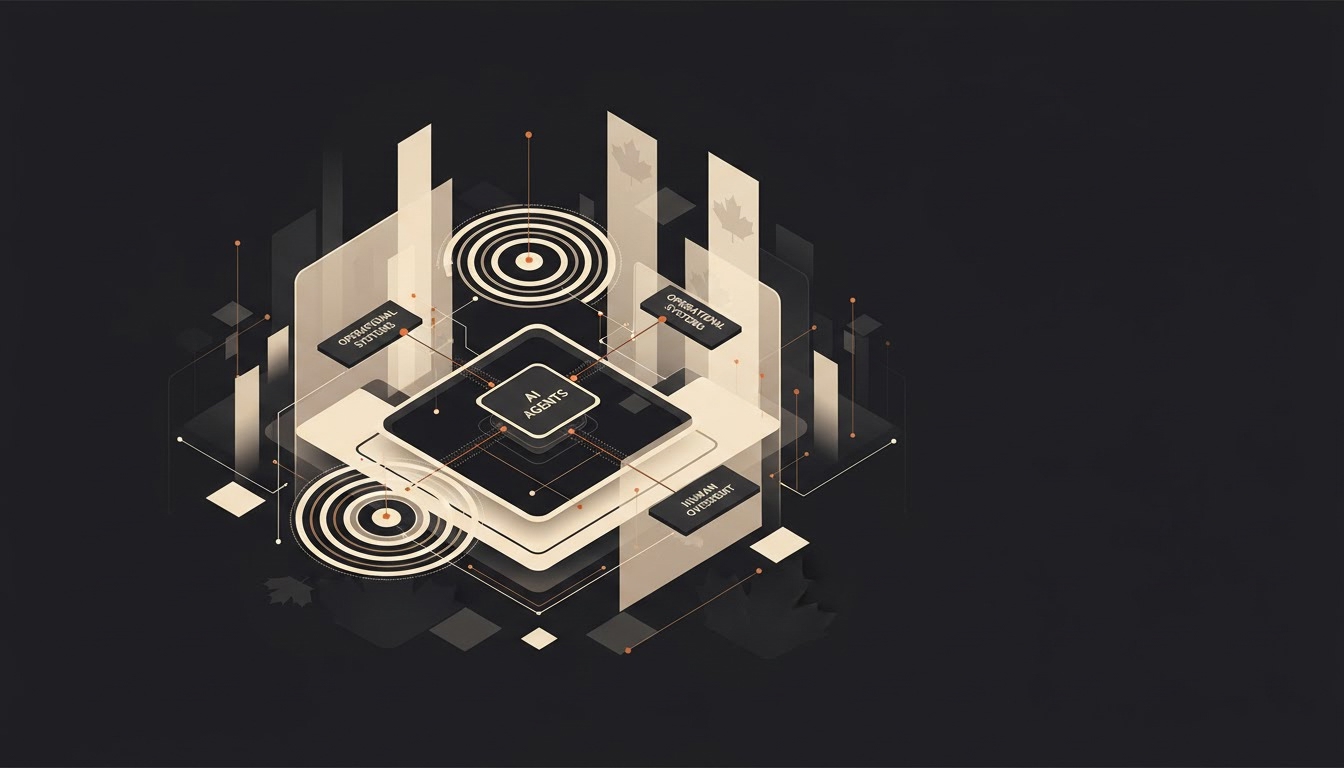
Canadian operations leaders face the critical task of integrating AI agents responsibly, balancing innovation with accountability. This requires a clear understanding of governance principles, especially when deploying managed AI agents that augment operational capacity within existing workflows.
Effective governance ensures that AI agents operate reliably, ethically, and in alignment with organizational values, without mistaking voluntary frameworks for legal mandates. This guide provides a practical framework for making informed decisions about AI agent oversight in a Canadian context.
Understanding the Canadian Context for AI Governance
Responsible AI governance in Canada is shaped by a blend of emerging legislation, voluntary frameworks, and ethical guidelines. While the Artificial Intelligence and Data Act (AIDA) is under development, it primarily targets high-impact systems and does not yet constitute universal private-sector law for all AI deployments.
Operations leaders must distinguish between mandatory legal requirements and best practice recommendations. Adopting voluntary frameworks, such as the NIST AI Risk Management Framework (AI RMF) [1], provides a structured approach to embedding trustworthiness into AI agent lifecycles, even without direct legal compulsion.
- Canadian legal landscape is evolving, not fully defined.
- Voluntary frameworks offer practical guidance.
- Distinguish legal mandates from best practices.
- NIST AI RMF provides a structured approach.
Differentiating AI Agent Delivery Models for Governance
The governance strategy for AI agents must align with their delivery model: internal build, platform configuration, or managed service. Each model presents distinct challenges and opportunities for oversight, impacting data access, accountability, and the scope of human review.
For managed AI agents, like those deployed by Kaza, governance shifts towards robust service level agreements, clear audit trails, and defined intervention points. This ensures that while operational capacity is enhanced, control and accountability remain firmly within the organization's purview.
- Governance varies by delivery model.
- Internal build offers full control.
- Managed agents require strong SLAs and auditability.
- Kaza's managed agents integrate into existing workflows.
Implementing Reusable Governance Practices with NIST AI RMF
The NIST AI RMF provides a practical, adaptable framework for managing AI risks across various deployment scenarios [1]. Its core functions—GOVERN, MAP, MEASURE, and MANAGE—offer a structured approach to integrating responsible practices into the entire AI agent lifecycle, from design to decommissioning.
Operations leaders can apply these functions to establish clear policies (GOVERN), identify risks (MAP), assess performance (MEASURE), and continuously improve (MANAGE). This systematic approach ensures that AI agents, including managed AI agents, operate within defined ethical and operational boundaries, fostering trust and reliability.
- NIST AI RMF offers adaptable governance structure.
- GOVERN: Establish policies and procedures.
- MAP: Identify and characterize AI risks.
- MEASURE: Evaluate AI system performance and impact.
Establishing Robust Human Review and Auditability
Effective AI governance hinges on establishing clear human review protocols and comprehensive auditability. For any AI agent, especially those impacting critical workflows, human oversight is essential for validating outputs, intervening in exceptions, and learning from failures. This prevents automation from becoming an unmonitored black box.
Implementing audit trails allows organizations to trace AI agent decisions and actions, providing transparency and accountability. This is particularly crucial for managed AI agents, where Kaza ensures that every action can be reviewed and understood, supporting continuous improvement and trust in operational capacity.
- Human review is critical for AI agent validation.
- Audit trails ensure transparency and accountability.
- Define intervention points for exceptions.
- Kaza's agents support comprehensive review.
Navigating Data Access, Failure Modes, and Organizational Change
Responsible AI governance requires careful consideration of data access, potential failure modes, and the organizational changes AI agents introduce. Secure data access protocols are paramount to protect sensitive information while enabling AI agent functionality. This includes defining data provenance and usage policies.
Proactive planning for failure modes, including identifying potential biases or errors, allows for the development of robust mitigation strategies and fallback procedures. Managing organizational change through clear communication and training ensures that teams adapt effectively to new workflows enhanced by AI agents, maintaining trust and operational reliability.
- Secure data access is fundamental.
- Plan for AI agent failure modes.
- Manage organizational change effectively.
- Ensure data provenance and usage policies.
The next decision for operations leaders is to select the appropriate AI agent delivery model that aligns with their specific workflow needs and governance capabilities. This choice should be driven by the required level of control over the AI agent's internal workings and the organization's capacity for in-house development and oversight.
If your workflow demands seamless integration with external expertise and robust auditability without extensive internal development, a managed AI agent model (e.g., Kaza) is justified. Conversely, if deep, proprietary technical control is paramount, an internal build is indicated. The key observation that would change this recommendation is a significant shift in internal technical resources or a change in regulatory requirements.
Frequently asked questions
How does Canadian public sector guidance apply to private companies using AI agents?
Canadian public sector guidance, like the Directive on Automated Decision-Making, offers valuable principles for responsible AI. While not legally binding for private companies, these principles can inform best practices for ethical AI deployment, data governance, and transparency within your organization's private workflows.
What is the role of human review when using managed AI agents?
Human review remains critical for managed AI agents. It involves validating agent outputs, intervening in edge cases, and providing feedback for continuous improvement. This ensures accountability, prevents unintended consequences, and maintains human oversight over automated workflows, enhancing overall operational reliability.
What evidence should a team retain for this choice?
Retain the case sample, workflow assumptions, human-review threshold, decision owner, and observed outcome. Those artifacts let the team verify the choice and revise it when the operating context changes.
Are voluntary AI governance frameworks sufficient for compliance in Canada?
Voluntary frameworks, such as the NIST AI RMF, are excellent for establishing robust internal governance and best practices. However, they are not a substitute for adhering to existing or future Canadian laws regarding data privacy (e.g., PIPEDA) or sector-specific regulations. They complement legal compliance by building trust.
What evidence should a team retain for this choice?
Retain the case sample, workflow assumptions, human-review threshold, decision owner, and observed outcome. Those artifacts let the team verify the choice and revise it when the operating context changes.