Adopting managed AI agents offers significant operational capacity, but it also introduces new governance challenges. For Canadian organizations, navigating responsible AI means understanding a landscape of evolving guidance, distinguishing between voluntary frameworks and specific legal requirements. This article provides a practical framework for executives and transformation leaders to implement robust governance.
Effective AI governance is not about blanket restrictions, but about enabling responsible innovation. It ensures that AI agents operate safely, ethically, and accountably within your existing workflows. The focus must be on practical measures that integrate oversight, auditability, and human review into the operational fabric, aligning with Canadian expectations for trust and transparency.
Establish Clear Scope Distinctions for Governance
Effective AI governance begins by distinguishing between voluntary best practices and legally binding obligations. While frameworks like the NIST AI Risk Management Framework [1] offer excellent guidance for trustworthiness, they are not, by themselves, Canadian law. Your organization's specific sector and jurisdiction will dictate actual legal compliance requirements, particularly concerning data privacy and consumer protection.
Understanding this distinction allows leaders to apply governance resources strategically. Focus rigorous legal and compliance reviews on areas where AI agents interact with regulated data or make decisions impacting individuals. For less sensitive internal workflows, voluntary frameworks provide a robust foundation for ethical and responsible deployment without unnecessary legal overhead.
- Voluntary frameworks (e.g., NIST AI RMF) provide best practices, not legal mandates.
- Legal obligations vary by Canadian sector and provincial jurisdiction.
- Prioritize legal review for AI agents handling sensitive data or critical decisions.
- Apply voluntary guidance broadly for internal, lower-risk workflows.
Implement Reusable Governance Practices Across Workflows
Reusable governance practices are essential for scaling AI agent deployments responsibly. Instead of reinventing the wheel for each new workflow, establish a core set of principles and procedures. These should cover data access, model transparency, performance monitoring, and human review protocols. Such an approach ensures consistency and reduces the overhead of governance.
For instance, every managed AI agent, regardless of its specific task, should operate under defined data access policies. Similarly, a standard for documenting an AI agent's purpose, limitations, and decision logic facilitates auditability. These foundational practices enable organizations to deploy new AI agents efficiently while maintaining a high standard of accountability and trust.
- Standardize data access policies for all AI agents.
- Define clear documentation requirements for AI agent purpose and logic.
- Establish consistent performance monitoring and bias detection protocols.
- Develop scalable human review processes for diverse AI agent outputs.
Integrate Accountable Human Review into AI Agent Workflows
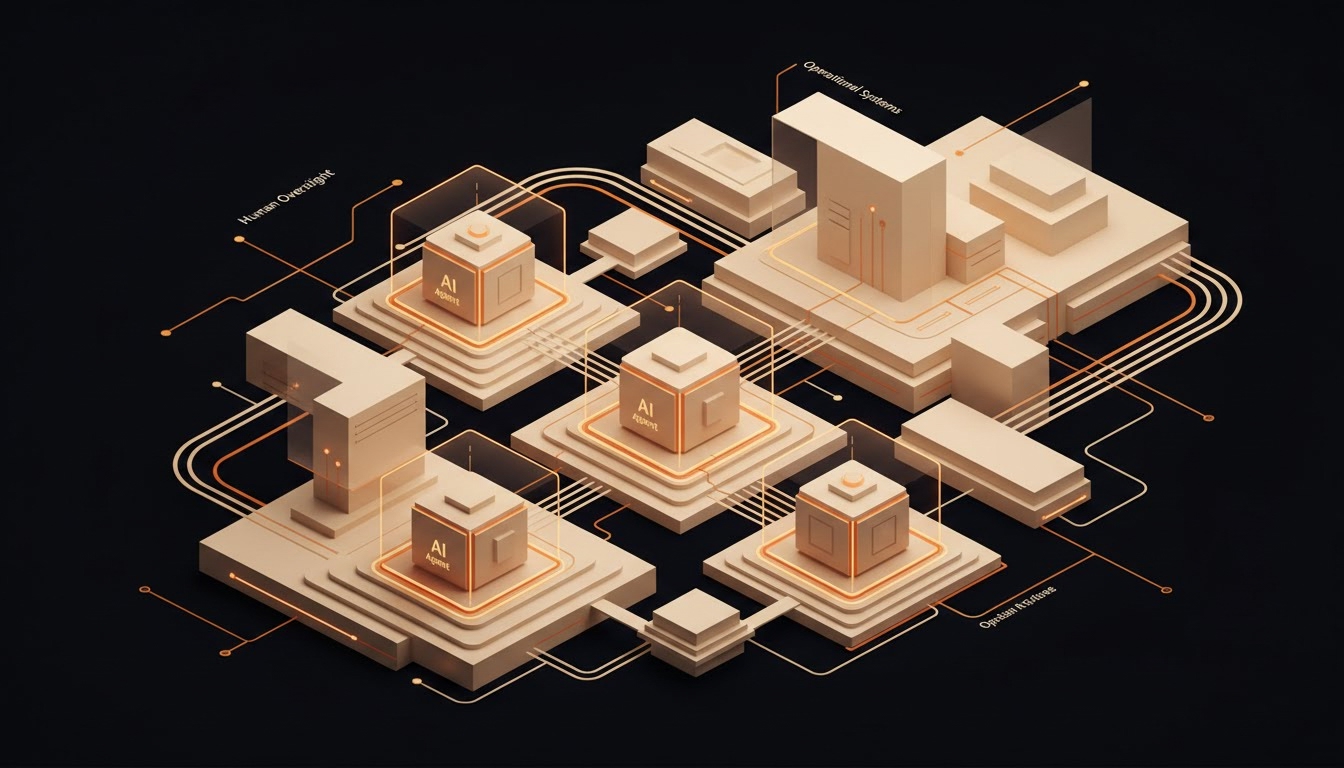
Accountable human review is a cornerstone of responsible AI governance, especially for managed AI agents. This means designing workflows where human oversight is not an afterthought but an integral component. For critical tasks, this might involve mandatory human approval before an AI agent's output is finalized or actioned, ensuring human accountability for outcomes.
Beyond approval, human review also encompasses monitoring AI agent performance, identifying potential biases, and intervening when necessary. Kaza's approach to managed AI agents emphasizes this by deploying systems that add practical execution capacity while maintaining clear points for human review and intervention, ensuring that humans remain in control of the operational outcomes.
- Design workflows with mandatory human approval for critical AI agent outputs.
- Implement continuous monitoring by humans to detect AI agent drift or errors.
- Establish clear protocols for human intervention and override capabilities.
- Ensure humans remain accountable for the final decisions influenced by AI agents.
Ensure Robust Auditability and Transparency of AI Agent Actions
Auditability is non-negotiable for trustworthy AI agent deployments. Every action taken by a managed AI agent, every data point accessed, and every decision made should be traceable. This requires comprehensive logging, version control for models, and clear documentation of training data and parameters. Such transparency builds trust and facilitates investigations into any unexpected outcomes.
A robust audit trail allows organizations to understand why an AI agent made a particular recommendation or took a specific action. This is crucial for debugging, demonstrating compliance, and explaining AI behaviour to stakeholders or regulators. Without this, organizations risk deploying 'black box' systems that undermine accountability and trust within their operational capacity.
- Implement comprehensive logging for all AI agent actions and data interactions.
- Maintain version control for AI models and their associated parameters.
- Document training data sources and methodologies used for AI agent development.
- Ensure audit trails are immutable and accessible for review and investigation.
Navigate the Legal Advice Boundary with Caution
It is crucial for executives to understand that this guidance provides a practical governance framework, not legal advice. While it touches upon regulatory considerations relevant to Canada, specific legal interpretations and compliance strategies must come from qualified legal counsel. Relying solely on general best practices for legal compliance can expose organizations to significant risks.
When deploying AI agents in areas with legal implications, such as privacy, data security, or consumer protection, always consult with legal experts. They can provide tailored advice on provincial and federal regulations, ensuring your AI governance framework meets all statutory requirements and mitigates specific legal liabilities. This boundary is critical for responsible deployment.
- Distinguish between practical governance guidance and formal legal advice.
- Consult qualified legal counsel for specific interpretations of Canadian AI regulations.
- Do not rely solely on general best practices for legal compliance.
- Seek legal expertise for AI agent deployments impacting privacy or consumer rights.
The next decision for leaders is to assess their current AI governance maturity against the proposed framework. This requires an honest evaluation of existing data access controls, audit capabilities, and human review protocols. If your organization lacks clear, documented processes for these elements, immediate action is warranted to build foundational governance.
The recommendation for a comprehensive, tiered governance framework stands firm unless your AI agent deployments are exclusively in workflows with zero human impact and no access to sensitive data. Any deviation from this 'zero impact, no sensitive data' threshold necessitates a structured approach to governance, ensuring that every managed AI agent deployment enhances operational capacity responsibly and accountably.
Frequently asked questions
How do Canadian privacy laws (like PIPEDA) apply to AI agents?
Canadian privacy laws, including PIPEDA and provincial equivalents, apply to AI agents handling personal information. Organizations must ensure consent for data collection, limit data use to stated purposes, and implement robust security safeguards. AI agents must be designed to respect these principles, with clear data governance and retention policies in place.
What is the difference between voluntary AI frameworks and legal requirements in Canada?
Voluntary frameworks, like the NIST AI RMF [1], offer guidelines for best practices in AI trustworthiness. Legal requirements, conversely, are binding laws (e.g., consumer protection acts, privacy statutes) that mandate specific behaviours and safeguards. Organizations must comply with laws while using voluntary frameworks to enhance responsible AI practices beyond the minimum legal threshold.
How can I ensure my AI agents are auditable?
To ensure auditability, design AI agents to log every action, decision, and data interaction. Implement version control for models and associated data. Document the AI agent's purpose, logic, and training data. This creates a transparent trail, allowing for reconstruction of events, debugging, and demonstrating compliance with governance policies and regulations.
What role does human review play in governing managed AI agents?
Human review is critical for governing managed AI agents by providing oversight, accountability, and ethical checks. It involves setting mandatory approval points for critical outputs, monitoring performance for drift or bias, and enabling human intervention to correct errors. This ensures that AI agents augment, rather than replace, human judgment, especially in high-stakes workflows.
How should we approach data access for AI agents to maintain trust?
Approach data access for AI agents with a 'least privilege' principle. Grant AI agents access only to the data absolutely necessary for their function. Implement strict access controls, encryption, and regular audits. Ensure data provenance is clear and that all data usage aligns with privacy policies and consent, fostering trust in the AI agent's operations.