Implementing responsible AI governance for managed AI agents in Canada requires a nuanced approach. While federal guidance and proposed legislation like the Artificial Intelligence and Data Act (AIDA) signal a clear direction, private sector organizations must carefully interpret these frameworks. The goal is to establish robust oversight that aligns with Canadian values of trust and safety, without misapplying public-sector mandates.
This guide provides IT, data, and security leaders with a practical framework to assess their specific workflows and deploy appropriate governance. It emphasizes distinguishing between voluntary best practices and legal requirements, focusing on observable workflow evidence. By doing so, organizations can build trust and ensure accountability for their AI agent deployments, enhancing operational capacity responsibly.
Understanding the Canadian AI Governance Landscape
Responsible AI governance in Canada is evolving, with federal initiatives like the Artificial Intelligence and Data Act (AIDA) proposing a risk-based approach for high-impact AI systems. While AIDA is not yet law and primarily targets federal jurisdiction and specific high-impact systems, it signals a broader expectation for accountability and transparency. Private sector organizations should monitor these developments, but recognize that current public-sector guidelines are not direct legal mandates for all private operations.
Voluntary frameworks, such as the National Institute of Standards and Technology (NIST) AI Risk Management Framework (AI RMF) [1], offer valuable guidance for incorporating trustworthiness into AI system design and use. These frameworks, while not legally binding in Canada, provide practical structures for managing AI risks, including GOVERN, MAP, MEASURE, and MANAGE functions. They help organizations establish internal policies and processes that align with responsible AI principles, fostering trust and mitigating potential harms.
- AIDA proposes a risk-based approach for high-impact AI systems.
- NIST AI RMF provides voluntary, practical risk management guidance.
- Public sector guidelines inform, but do not universally bind, private operations.
- Distinguish between proposed legislation, voluntary frameworks, and current law.
Scoping AI Agent Governance by Workflow Risk
Effective AI agent governance is not a one-size-fits-all solution; it must be scoped to the specific workflow and its inherent risks. The criticality of the workflow, the sensitivity of data processed, and the level of autonomy granted to the AI agent are primary determinants. A managed AI agent handling public data for internal reporting requires different oversight than one making autonomous financial transactions or critical operational decisions. Over-governing low-risk workflows can stifle innovation and efficiency.
Begin by classifying workflows based on their potential impact on individuals, the organization, and stakeholders. This involves assessing data privacy implications, the potential for bias, and the severity of consequences from an erroneous decision. This risk-based approach ensures that governance resources are allocated effectively, focusing stringent controls where they are most needed, thereby enhancing the operational capacity of your AI agents responsibly.
- Tailor governance based on workflow criticality and data sensitivity.
- Assess AI agent autonomy and potential impact of errors.
- Avoid over-governing low-risk, non-critical workflows.
- Prioritize controls for high-impact, sensitive data processes.
Implementing Reusable Governance Practices for AI Agents
To ensure consistent and scalable governance for managed AI agents, organizations should develop reusable practices that can be applied across various deployments. These practices should include clear policies for data access, model validation, performance monitoring, and incident response. Establishing standardized templates for risk assessments and impact analyses allows for efficient and repeatable evaluation of new AI agent integrations. This systematic approach reduces overhead and promotes a culture of responsible AI use.
Key reusable practices involve defining roles and responsibilities for human review, establishing audit trails for all AI agent actions and decisions, and setting thresholds for human intervention. Regular training for staff on AI ethics and governance principles is also crucial. By embedding these practices into the operational fabric, organizations can ensure that every AI agent deployment, from simple automation to complex operational capacity, adheres to established standards of trust and accountability.
- Develop standardized policies for data access and model validation.
- Create templates for risk assessments and impact analyses.
- Define clear roles for human review and intervention thresholds.
- Implement robust audit trails for all AI agent actions.
Ensuring Accountable Human Review and Oversight
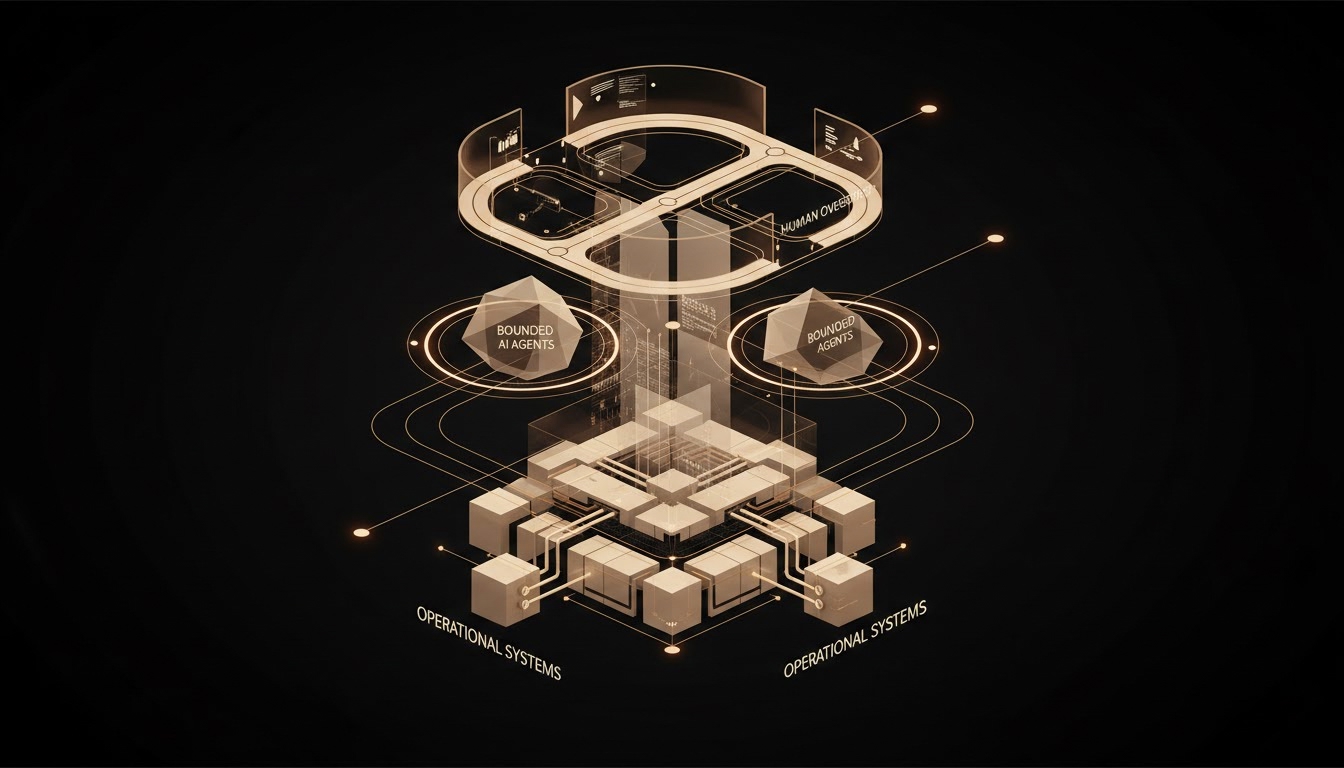
Human review remains a cornerstone of responsible AI governance, particularly for managed AI agents operating in critical workflows. It is essential to design clear points for human oversight, ensuring that individuals can understand, challenge, and override AI agent decisions when necessary. This is not merely about compliance; it's about maintaining operational control and accountability. The nature and frequency of human review should directly correlate with the workflow's risk profile, ranging from periodic spot-checks to mandatory pre-action approvals.
Establishing an auditable record of human interventions and AI agent performance is critical for accountability. This includes logging all decisions made by the AI agent, the rationale behind them, and any human overrides or adjustments. Such detailed auditability supports continuous improvement, helps identify potential biases, and provides necessary evidence for regulatory scrutiny or internal investigations. Kaza's managed AI agents are designed to integrate seamlessly with these human review and oversight mechanisms.
- Design clear human oversight points for all AI agent decisions.
- Vary human review frequency based on workflow risk.
- Maintain auditable records of AI agent actions and human interventions.
- Ensure human reviewers can understand, challenge, and override AI decisions.
Navigating the Legal Advice Boundary
Organizations must be acutely aware of the boundary between operational governance guidance and legal advice. While this article provides practical frameworks for implementing responsible AI governance, it does not constitute legal counsel. Canadian regulations, including privacy laws like PIPEDA and provincial equivalents, apply to AI systems handling personal information. Proposed legislation like AIDA suggests future legal obligations for certain high-impact AI systems, but its final form and scope are still under development.
For specific legal interpretations or to ensure full compliance with current and emerging Canadian laws, organizations should consult qualified legal professionals. Kaza focuses on the practical deployment and operational capacity of managed AI agents, designing systems that facilitate governance and auditability. However, the ultimate responsibility for legal compliance rests with the deploying organization, requiring dedicated legal review of their specific AI agent applications and data handling practices.
- Operational governance guidance is distinct from legal advice.
- Consult legal professionals for specific compliance with Canadian laws.
- PIPEDA and provincial privacy laws apply to AI handling personal data.
- AIDA is proposed legislation; its legal implications are still evolving.
Navigating responsible AI governance in Canada requires a strategic, workflow-centric approach that balances innovation with accountability. By carefully assessing workflow risks, implementing reusable governance practices, and ensuring robust human review, organizations can confidently deploy managed AI agents. Distinguishing between voluntary frameworks and legal mandates is crucial for effective compliance and building trust.
Your next decision should be to conduct a comprehensive risk assessment for each workflow targeted for AI agent deployment, using the provided framework. If the assessment reveals high-impact risks without adequate human oversight or auditability, redesign the workflow or the AI agent's role to incorporate necessary controls. If the workflow involves sensitive data or autonomous critical decisions, an immediate legal review is warranted before deployment.
Frequently asked questions
How do Canadian privacy laws like PIPEDA apply to AI agents?
PIPEDA (Personal Information Protection and Electronic Documents Act) and similar provincial laws apply whenever AI agents collect, use, or disclose personal information. Organizations must ensure consent, protect data, and maintain accountability for personal data processed by their AI systems. This includes transparent data handling practices and robust security measures for managed AI agents.
What is the difference between voluntary AI frameworks and legal requirements in Canada?
Voluntary frameworks, like the NIST AI RMF [1], offer best practices and guidance for responsible AI development and deployment. Legal requirements, such as PIPEDA or future AIDA provisions, are binding laws with penalties for non-compliance. While frameworks inform good practice, they are not a substitute for legal obligations. Organizations must meet legal minimums while striving for best practices.
How can we ensure our AI agents are auditable for governance purposes?
To ensure auditability, design AI agents to log all actions, decisions, and the data inputs used. Implement clear version control for models and configurations. Establish accessible audit trails that record human interventions, overrides, and performance metrics. This allows for retrospective analysis, accountability, and demonstrates adherence to governance policies for your operational capacity.
When should an AI agent's decision always require human approval?
Human approval should always be required when an AI agent's decision has high-stakes implications, such as significant financial impact, legal consequences, safety risks, or direct impact on an individual's rights. Workflows involving sensitive personal data or critical operational control also warrant mandatory pre-action human review to ensure accountability and mitigate risks.
Does Canada's AIDA apply to all private sector AI deployments?
No, the proposed Artificial Intelligence and Data Act (AIDA) is designed to apply to 'high-impact' AI systems, which are specifically defined within the legislation. It is not intended to cover all AI deployments in the private sector. Organizations should monitor its progress and consult legal experts to determine if their specific AI agent applications fall under its scope once it becomes law.