Integrating managed AI agents into an organization's operating model offers significant gains in operational capacity, but it also introduces new governance challenges. Unlike simple automation or isolated chat tools, AI agents exhibit a degree of autonomy, requiring a structured approach to ensure they align with organizational values, regulatory requirements, and performance expectations.
Effective governance for AI agents moves beyond theoretical principles to establish concrete controls and accountable routines. This framework addresses critical aspects such as data access, decision-making authority, human review protocols, and auditability, providing leaders with the tools to manage risk and build trust in their AI-driven operations.
Defining Governance Layers for Managed AI Agents
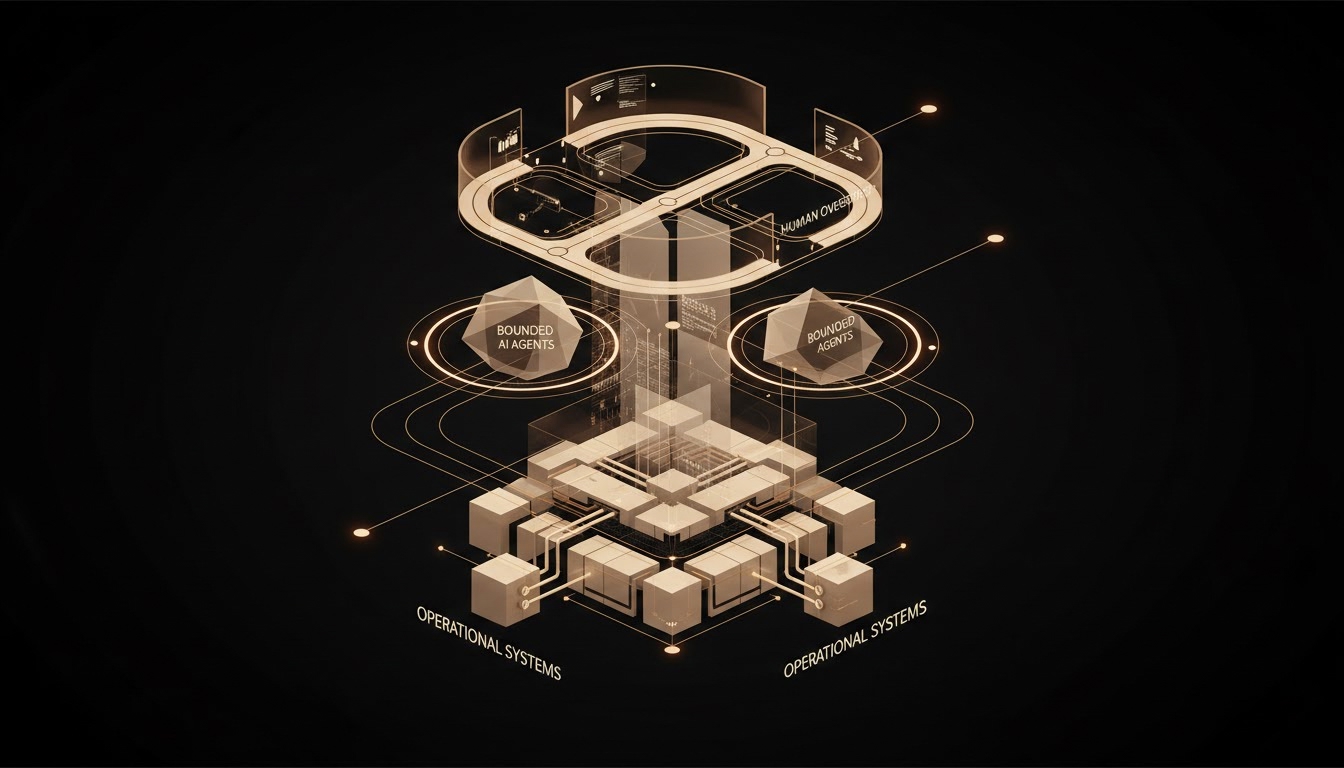
Effective governance for managed AI agents requires a multi-layered approach, distinguishing between strategic, operational, and technical oversight. This structure ensures that decisions are made at the appropriate level, from high-level policy setting to day-to-day operational execution. Each layer addresses distinct aspects of risk and trust, aligning agent activities with organizational objectives.
Strategic governance defines the overarching vision and ethical boundaries for AI use, while operational governance translates these into actionable processes and performance metrics. Technical governance, in turn, focuses on the secure and reliable functioning of the agents themselves, including data integrity and system security. This division of responsibility prevents gaps in oversight.
- Strategic: Policy, ethics, enterprise risk.
- Operational: Workflow integration, performance, compliance.
- Technical: Data security, model integrity, system reliability.
Establishing Clear Decision Rights and Accountability
Clarity in decision rights is paramount for governing AI agents, especially given their capacity for autonomous action. Organizations must explicitly define who is accountable for agent deployment, modification, and the handling of exceptions. This ensures that human oversight is maintained at critical junctures, preventing unintended consequences and fostering trust in agent operations.
Decision rights should cover scenarios such as approving new agent workflows, modifying agent behaviour, overriding agent decisions, and decommissioning agents. Without these clear lines of authority, accountability can become diffused, leading to governance gaps. This is particularly important for managed AI agents that interact with sensitive data or critical systems.
- Who approves agent deployment?
- Who can modify agent parameters?
- Who addresses agent errors or exceptions?
- Who is responsible for agent performance?
Implementing Evidence and Review Cadences
Robust governance for AI agents relies on a consistent cadence of evidence collection and review. This includes regular monitoring of agent performance, auditing their decision logs, and scheduling human-in-the-loop interventions. Such practices provide the necessary data to assess agent effectiveness, identify biases, ensure compliance, and maintain overall system integrity.
Review cadences should be tailored to the agent's criticality and risk profile, ranging from continuous monitoring for high-impact agents to periodic audits for less critical functions. Evidence, such as audit trails of agent actions and decisions, is crucial for demonstrating accountability and for continuous improvement of agent performance and governance protocols.
- Automated performance monitoring.
- Regular audit log reviews.
- Scheduled human-in-the-loop checks.
- Post-incident analysis and reporting.
Distinguishing Managed AI Agents from Simple Automation
It is crucial to differentiate the governance needs of managed AI agents from those of simpler, rule-based automation or basic chat tools. Managed AI agents, by design, possess a greater degree of autonomy, adaptability, and interaction with dynamic environments. This requires a more sophisticated governance framework that accounts for emergent behaviours and complex decision-making processes.
Unlike fixed automation, AI agents can learn and adapt, making their outputs less predictable. Governance must therefore focus on continuous monitoring, explainability, and robust human review mechanisms to manage the inherent variability. This distinction is key to designing controls that are proportionate to the actual risks posed by agent autonomy.
- Autonomy and adaptability.
- Dynamic environment interaction.
- Complex decision-making.
- Potential for emergent behaviour.
Ensuring Auditability and Transparency in Agent Operations
A cornerstone of trust in AI agent deployments is their auditability and transparency. Every action and decision made by an AI agent must be logged, traceable, and explainable to human operators and auditors. This capability is essential for diagnosing issues, demonstrating compliance with internal policies and external regulations, and fostering accountability within the organization.
Implementing robust logging mechanisms that capture inputs, outputs, and intermediate steps of an agent's decision process is non-negotiable. This evidence supports post-incident analysis, performance optimization, and regulatory reporting. The NIST AI Risk Management Framework emphasizes the importance of auditability for trustworthiness [1].
- Comprehensive action logging.
- Traceability of decisions.
- Explainability of outcomes.
- Support for regulatory compliance.
Establishing a robust governance framework for managed AI agents is not merely a compliance exercise; it is fundamental to building trust and realizing the full operational capacity these agents offer. By defining clear governance layers, assigning explicit decision rights, and implementing rigorous evidence and review cadences, organizations can confidently deploy AI agents while mitigating risks.
Leaders should prioritize translating governance principles into concrete, named controls and accountable routines. This structured approach, grounded in auditability and human oversight, provides the necessary foundation for responsible AI adoption. A well-defined framework ensures that AI agents operate effectively, ethically, and in alignment with organizational objectives, fostering long-term success.
Frequently asked questions
What is the primary difference between AI agent governance and general IT governance?
AI agent governance specifically addresses the unique challenges of autonomous, adaptive systems, focusing on emergent behaviour, data bias, and dynamic decision-making. General IT governance primarily covers infrastructure, data security, and system reliability, while AI governance adds layers for algorithmic accountability and ethical considerations.
How does human review integrate into AI agent governance?
Human review is a critical control point. It involves defining specific triggers for human intervention, such as high-risk decisions, unusual outputs, or exceptions to normal operations. This ensures that a human can assess, validate, or override agent actions, maintaining ethical oversight and preventing unintended consequences.
What are 'decision rights' in the context of AI agent governance?
Decision rights explicitly assign authority and accountability for various aspects of an AI agent's lifecycle. This includes who can approve agent deployment, modify its parameters, handle errors, or decommission it. Clear decision rights prevent ambiguity and ensure responsible management of agent operations.
Why is auditability so important for AI agents?
Auditability is crucial for trust and accountability. It ensures that every action and decision an AI agent makes can be traced, reviewed, and explained. This is vital for diagnosing performance issues, demonstrating compliance with regulations, and providing transparency to stakeholders, especially in sensitive or critical workflows.
How can an organization start building an AI agent governance framework?
Begin by assessing current workflows and identifying areas where managed AI agents could provide operational capacity. Then, define the strategic, operational, and technical governance layers relevant to your organization. Establish clear decision rights and implement a robust evidence and review cadence, drawing on frameworks like NIST's AI RMF [1].