Implementing an effective governance framework for managed AI agents is crucial for operational leaders seeking reliable, trustworthy, and scalable automation. Generic principles alone are insufficient; success hinges on translating these into specific, actionable controls and integrating them into daily operations. This requires a pragmatic approach that addresses the unique characteristics of AI agents beyond simple automation.
This framework provides a structured approach to operationalizing AI agent governance, focusing on named controls, clear decision rights, and established review cadences. By moving from abstract guidelines to concrete, auditable routines, organizations can build confidence in their AI deployments, ensuring they enhance, rather than compromise, operational capacity and service quality.
Establishing Governance Layers and Control Types
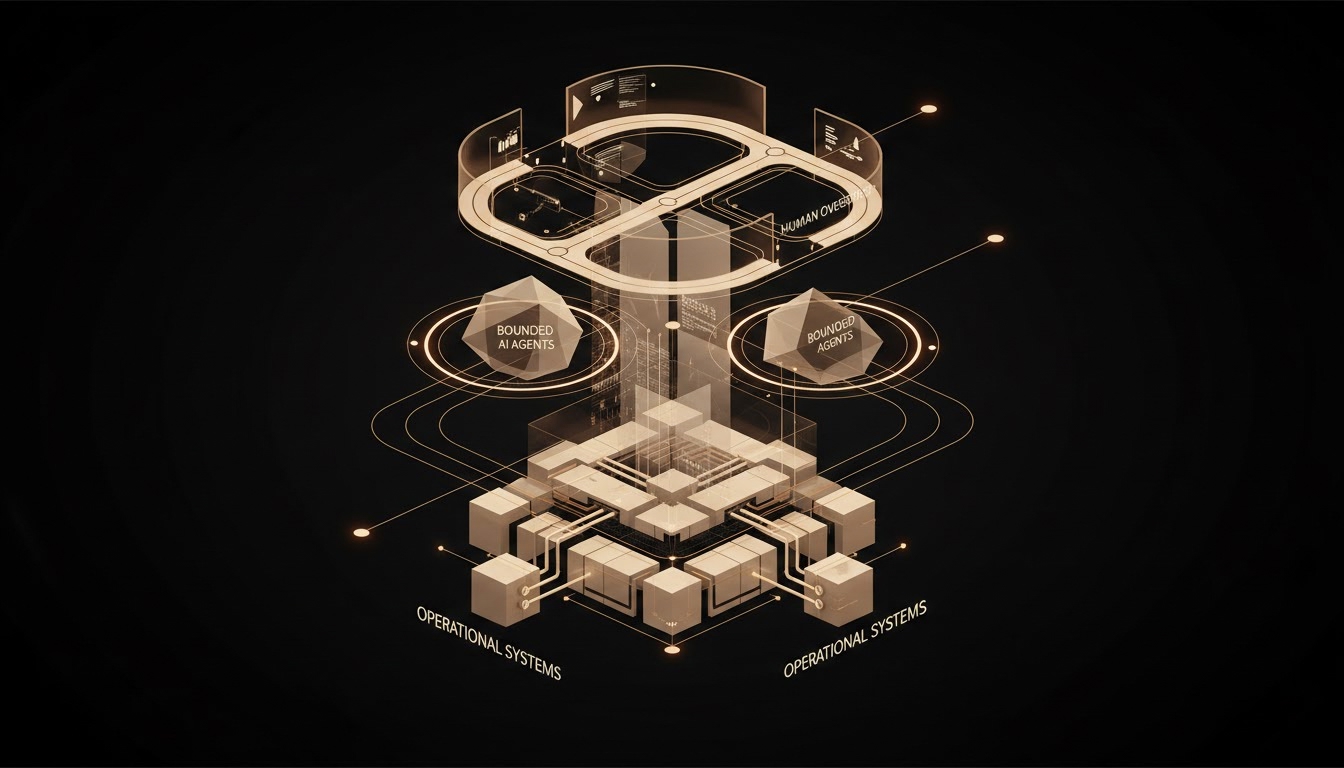
Effective AI agent governance requires distinct layers, each with specific responsibilities and control types. The strategic layer sets overarching policies and risk appetite, while the operational layer translates these into actionable processes. The technical layer implements the controls within the AI agent's environment, ensuring compliance at the execution level. This layered approach ensures comprehensive coverage from policy to execution.
Controls must be specific and named, moving beyond generic statements like 'ensure fairness.' Instead, consider 'bias detection and mitigation routine' or 'data provenance verification control.' This precision allows for clear implementation, measurement, and auditability. The NIST AI Risk Management Framework (AI RMF) outlines core functions like GOVERN and MANAGE, providing a voluntary framework for incorporating trustworthiness [1].
- Strategic Layer: Policy, risk appetite, ethical guidelines.
- Operational Layer: Process design, incident response, human review protocols.
- Technical Layer: Access management, data encryption, model versioning.
- Named Controls: Specific, measurable, auditable actions.
Defining Clear Decision Rights for Accountability
Accountability in AI agent operations hinges on clearly defined decision rights. This means specifying who is authorized to make decisions at each stage of an AI agent's lifecycle, from design and deployment to monitoring and retirement. Without this clarity, critical decisions can be delayed, or worse, fall through the cracks, leading to operational inefficiencies and increased risk exposure.
Decision rights should cover aspects like approving model changes, authorizing data access, initiating human review interventions, and signing off on performance thresholds. These rights must be documented and communicated across all relevant teams, including operations, IT, legal, and business stakeholders. This ensures that every action, or inaction, has an identifiable owner, fostering a culture of responsibility.
- Design Phase: Data access, model selection, ethical review.
- Deployment Phase: Release approval, integration validation.
- Monitoring Phase: Intervention triggers, performance threshold adjustments.
- Retirement Phase: Decommissioning approval, data archiving.
Implementing Evidence and Review Cadence
To ensure AI agents operate within governance parameters, a robust system for collecting evidence and conducting regular reviews is essential. This involves defining what constitutes 'evidence' of compliance for each control, such as audit logs, performance reports, human intervention records, or data lineage documentation. Without concrete evidence, verifying adherence to policies becomes subjective and unreliable.
Establishing a clear review cadence is equally important. This includes daily operational checks, weekly performance reviews, monthly compliance audits, and quarterly strategic governance meetings. The frequency and depth of reviews should align with the AI agent's criticality and risk profile. This systematic approach allows for early detection of deviations and continuous improvement of governance practices.
- Evidence: Audit logs, performance metrics, human override records.
- Review Cadence: Daily checks, weekly performance, monthly compliance, quarterly strategy.
- Automated Reporting: Dashboards for real-time control status.
- Incident Reporting: Structured process for deviations.
Integrating Accountable Routines into Workflows
Governance is not a static document; it's a dynamic set of practices embedded within daily workflows. Accountable routines are the operational mechanisms that translate controls and decision rights into consistent actions. This means integrating governance checks directly into existing operational processes, rather than treating them as separate, burdensome tasks. For managed AI agents, this is particularly important given their continuous operation.
For example, a routine might involve a daily automated check of AI agent output against a baseline, triggering a human review if deviations exceed a defined threshold. Another routine could be a weekly review of human intervention logs by a team lead. These routines must be clearly documented, assigned to specific roles, and regularly audited to ensure they are being followed effectively, reinforcing accountability.
- Daily Checks: Automated performance and anomaly detection.
- Weekly Reviews: Human intervention logs, minor configuration changes.
- Monthly Audits: Compliance with data access policies, security logs.
- Quarterly Reviews: Strategic alignment, risk assessment updates.
Distinguishing AI Agent Governance from Simple Automation
While simple automation follows predefined rules, managed AI agents exhibit adaptive learning and a degree of autonomy, necessitating a more sophisticated governance approach. Unlike fixed scripts, AI agents can evolve their behaviour based on new data, introducing emergent risks that require continuous monitoring and adaptive controls. This distinction is critical for operations leaders.
Governance for AI agents must account for their ability to learn, reason, and make decisions within defined parameters. This includes controls for model drift, explainability, and the calibration of human review thresholds. Kaza diagnoses workflows, designs the right system, and deploys it into existing tools, recognizing that AI agent governance is an ongoing process of improvement, not a one-time setup.
- Adaptive Learning: Requires continuous monitoring for drift.
- Autonomy: Demands clear human-in-the-loop protocols.
- Emergent Risks: Necessitates dynamic risk assessment.
- Explainability: Controls for understanding AI agent decisions.
Operationalizing AI agent governance is a continuous journey, not a one-time project. By translating abstract principles into named controls, establishing clear decision rights, and embedding accountable routines into workflows, operations leaders can build a robust framework. This approach ensures managed AI agents enhance operational capacity reliably and responsibly, fostering trust across the organization.
The commitment to precise controls, transparent evidence, and consistent review cadences empowers organizations to harness the full potential of AI agents while mitigating inherent risks. This pragmatic, control-centric framework provides the necessary structure for confident and scalable AI agent deployment, aligning with Kaza's approach to responsible AI integration.
Frequently asked questions
How do I start implementing an AI agent governance framework?
Begin by identifying critical workflows where AI agents will operate and assess their risk profile. Then, define specific governance layers (strategic, operational, technical) and assign decision rights. Translate high-level principles into named controls, focusing on auditability and human review. Kaza can help diagnose workflows and design suitable systems.
What is the role of human review in AI agent governance?
Human review is a critical control point, especially for high-risk or sensitive decisions. It ensures ethical compliance, validates AI agent outputs, and provides oversight for learning systems. Define clear thresholds and protocols for when human intervention is required, ensuring it's integrated seamlessly into operational workflows for maximum effectiveness.
How does an AI agent governance framework differ from general IT governance?
While sharing some principles, AI agent governance specifically addresses the unique characteristics of AI, such as adaptive learning, potential for bias, and emergent behaviours. It focuses on controls for model drift, explainability, and dynamic risk management, which are not typically covered by traditional IT governance frameworks for static systems.
What evidence should I collect to demonstrate compliance with AI agent governance?
Key evidence includes comprehensive audit logs of AI agent actions and decisions, performance metrics, records of human interventions and overrides, data provenance documentation, and change management logs for model updates. This evidence supports internal audits, external compliance checks, and provides transparency into AI agent operations.
How can I ensure my AI agent governance framework remains effective over time?
Ensure effectiveness through continuous monitoring, regular review cadences, and an adaptive approach. Periodically reassess the framework against evolving risks, new AI agent capabilities, and organizational changes. Integrate feedback loops from human review and performance data to refine controls and decision rights, fostering ongoing improvement.